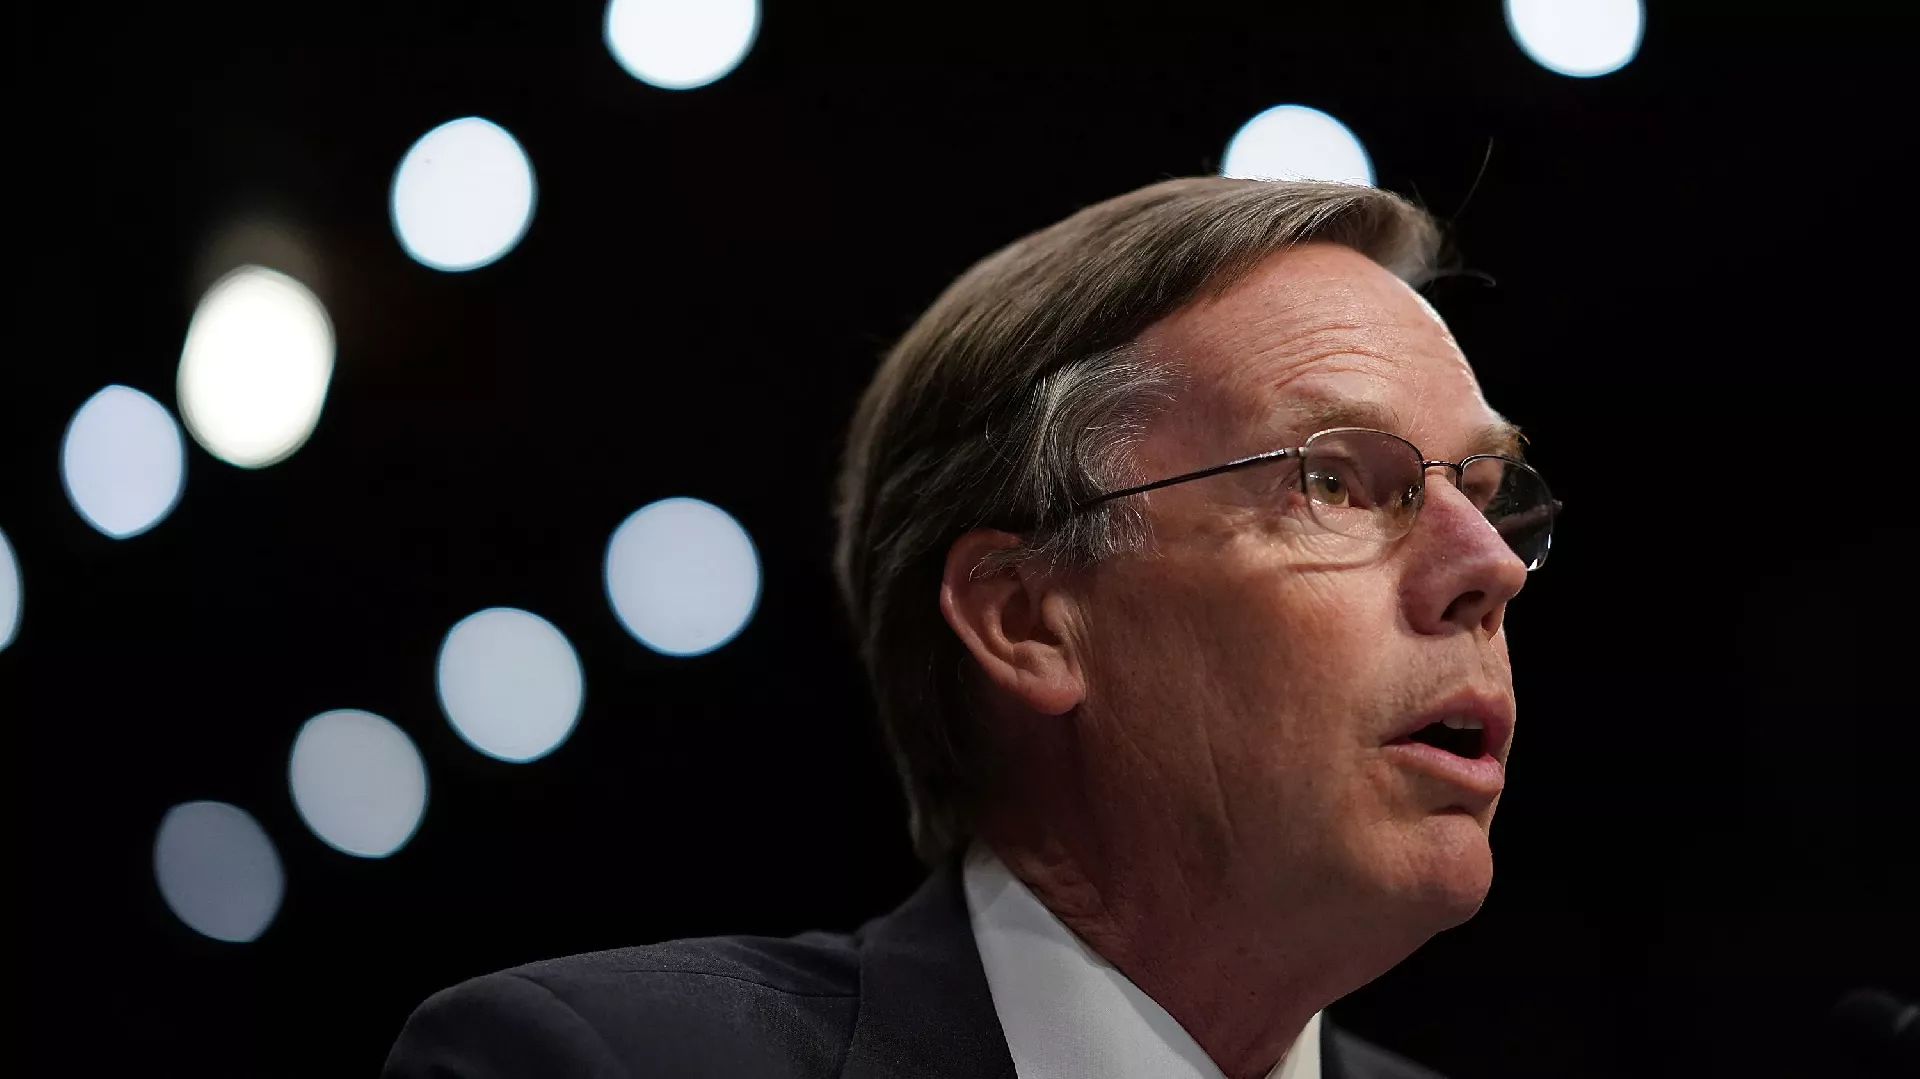
(Patria) - Hackers linked to Beijing accessed the email account of the US Ambassador to China, Nicholas Burns, in a spying operation believed to have compromised at least hundreds of thousands of individual US government emails, the Wall Street Journal (WSJ) reported.
Daniel Kritenbrink, Assistant Secretary of State for East Asian Affairs, was also hacked in the broader spying operation that Microsoft uncovered earlier this month, the report said, citing people familiar with the matter.
When asked about the reported compromise of the two diplomats' accounts, the State Department declined to provide details and said an investigation into the spying operation was ongoing, Reuters reported.
Before the WSJ report emerged, Kritenbrink was asked at a congressional hearing on US policy in China whether he could rule out that his or his staff's emails had been targeted by Microsoft hacks.
"I cannot comment on an FBI-led investigation, but no, I will not rule that out," Kritenbrink said.
Burns and Kritenbrink join US Commerce Secretary Gina Raimondo as the only publicly named victims of the spying campaign, which led Washington's top diplomat to warn his Chinese counterpart.
China's Ministry of Foreign Affairs previously called the earlier accusations "disinformation."
Microsoft said last week that Chinese hackers had breached one of its digital keys and exploited a flaw in its code to steal emails from US government agencies and other clients.
The incident has put Microsoft's security practices under scrutiny, with officials and lawmakers calling on the company to make its highest level of digital audit, also known as logging, available to all its clients for free. Microsoft said in a statement late on Thursday that it accepted the criticism.
Last week, White House National Security Council spokesperson Adam Hodge said the breach of Microsoft's cloud security "affected unclassified systems," without providing further details.
"Officials immediately contacted Microsoft to find the source and vulnerability in their cloud service," Hodge added.
The State Department "detected anomalous activity" and "immediately took steps to secure our systems," a department spokesperson said in a statement at the time.
Komentari (0)
Prijavite se za komentiranje
PrijavaJos nema komentara. Budite prvi!
Minuta
Sve →Iz drugih kategorija
High Representative Not Elected: Germans, French and British Sabotaged Americans, New Attempt at End of June
ČOVIĆ WITHOUT MERCY: How Those Who Brought Ademović to Office Created a Political Hell for Him
Sunny Saturday, quite warm
Tragedy in Albanian resort: Two minors drown